Модернизация безопасности периметра: масштабируемые периметры с помощью средств управления услугами VPC
Story summary
Агенты представляют собой фундаментальный сдвиг в облачных операциях. Они могут действовать от имени пользователей или автономно, принимать недетерминированные решения и запрашивать данные между проектами с беспрецедентной скоростью и масштабом. Поскольку агенты представляют собой отдельную категорию нечеловеческой идентичности (NHI), им требуется уникальная система безопасности.
📌 Key Highlights & Takeaways
- Агенты представляют собой фундаментальный сдвиг в облачных операциях.
- Они могут действовать от имени пользователей или автономно, принимать недетерминированные решения и запрашивать данные между проектами с беспрецедентной скоростью и масштабом.
- Поскольку агенты представляют собой отдельную категорию нечеловеческой идентичности (NHI), им требуется уникальная система безопасности.
Agents represent a fundamental shift in cloud operations. They can act on behalf of users or autonomously, make non-deterministic decisions, and request data across projects at unprecedented speed and scale. Because agents are a distinct category of non-human identity (NHI), they require unique secure-by-default guardrails.
Traditional, manually-operated network perimeters are vulnerable to today’s machine-speed attacks. Overly permissive perimeters, built to avoid blocked connections, increase the risk of unauthorized data theft, but overly strict perimeters stall development under a flood of access denials.
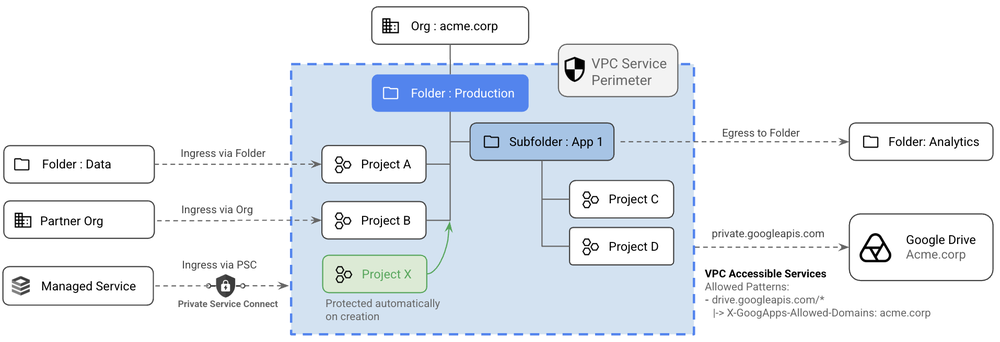
Today, we're excited to announce key enhancements to VPC Service Controls (VPC-SC) that make perimeters easier to create, maintain, and scale. You can now add folders to perimeter membership, so that projects contained in them inherit policy. You can also manage granular exceptions and resolve denials with guided, scoped remediation.
The result is data protected by default, so you can scale autonomous agents across your enterprise without letting data leave your perimeter. This update is generally available, and at no additional cost.
VPC-SC provides a context-aware network security perimeter around your Google Cloud deployment, designed to secure your organization against data theft, even in the event of compromised credentials, identity and access management (IAM) misconfigurations, and insider threats. By extending network-layer protection across service-to-service interactions in Google Cloud's infrastructure, VPC-SC goes beyond traditional firewalls and creates an additional layer of defense that prevents access outside your corporate network — and is now easier for your organization to manage.
Cloud administrators configuring VPC-SC can now include folders in perimeter membership , automatically extending the folder’s access policy to every project and nested subfolder it contains. New workloads can inherit protection by default, with no further modification.
Perimeter membership updates when a project is moved, simplifying lifecycle maintenance. Security coverage follows the resource hierarchy that your organization already governs, and compliance verification requires only confirming that the resource is located in the correct part of the hierarchy.
Dry-run mode also supports folder membership, helping administrators evaluate the effect of a hierarchy-wide perimeter against live traffic before enforcement.
Cryptographic Security & Key Generator
Generate entropy-tested high-security keys and encryption-grade tokens.
Source: Cloud Blog.
Read the full story at the original source ↗
For questions: mrsmithcons@gmail.com.
❓ Frequently Asked Questions (Cloud Architecture Briefing)
What makes this Cloud Architecture feature significant for FreeSky Cloud readers?
Our editorial team tracks verified source corroboration, technical specifications, and cultural resonance to deliver comprehensive analytical coverage.
How frequently is this coverage updated?
Our 24/7 automated monitoring desk updates breaking developments, verified media telemetry, and community commentary in real-time.
Where can readers follow ongoing developments on Модернизация безопасности периметра: масштабируемые периметры с помощью средств управления услугами VPC?
Bookmark this page or subscribe to our verified RSS feed for instant breaking alerts and in-depth analyses.
☁️ Complete Cloud Credit Application Guide & Architecture Specs
Direct application templates, fast-track partner codes, and architecture benchmarks.
⚡ Access Cloud Playbook ➔More from FreeSky Cloud

MI5 warns of rising threats to Britain as foreign plots and AI reshape security risks
MI5 warns of rising threats to Britain as foreign plots and AI reshape security risks From foreign-backed atta...
 🤖 WinBar AI
Боты для ставок на фондовые фонды на базе искусственного интеллекта могут выбирать акции быстрее и лучше, чем люди
Новое освещение, сообщает Reuters: боты для ставок на фондовые фонды на базе искусственного интеллекта могут в...
 🛰️ FreeSky Aerial
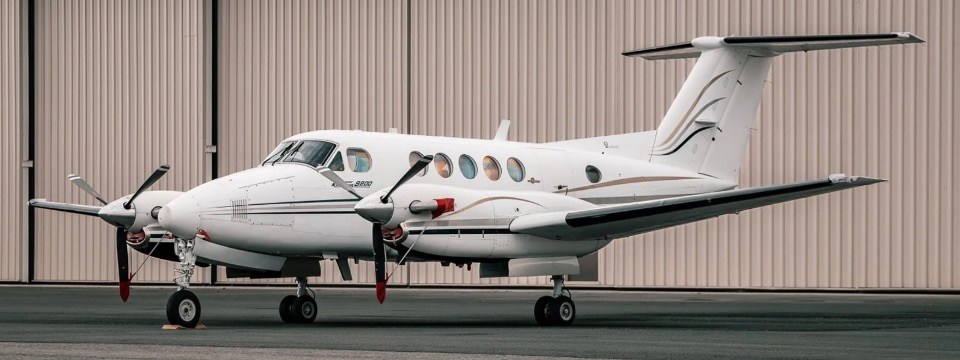
НАСА проведет полеты на малой высоте над сельскохозяйственными угодьями Техаса
Самолет NASA Dynamic Aviation A200 будет выполнять низколетящие исследовательские полеты над сельскохозяйствен...
From Animation to Reality: See Starship Deploy Satellites in Orbit
What was once just an animation is now a breathtaking reality. This epic video shows SpaceX's Starship success...