Investigating Ephemeral Supply Chain Tampering
Story summary
Written by: Tyler McLellan Introduction Google Threat Intelligence Group (GTIG) and Mandiant investigated a software supply chain compromise campaign targeting the update infrastructure belonging to AOMEI Technology between April 2026 and July 2026. The threat actor conducted repeated, short-burst c
📌 Key Highlights & Takeaways
- Written by: Tyler McLellan Introduction Google Threat Intelligence Group (GTIG) and Mandiant investigated a software supply chain compromise campaign targeting the update infrastructure belonging to AOMEI Technology between April 2026 and July 2026.
- The threat actor conducted repeated, short-burst c
Google Threat Intelligence Group (GTIG) and Mandiant investigated a software supply chain compromise campaign targeting the update infrastructure belonging to AOMEI Technology between April 2026 and July 2026. The threat actor conducted repeated, short-burst configuration tampering against AOMEI origin servers. Each tampering window remained active for only five to ten minutes before reverting to authentic versions. This is the first time that we have encountered a software supply chain compromise that was implemented with these very short windows, effectively evading traditional point-in-time triage and automated file scanning.
The campaign delivered a multi-stage payload chain involving the newly tracked CROSSROAD downloader and SHINYROAD backdoor. The threat actor iteratively modified its tradecraft, pivoting its staging infrastructure from cloud providers to dedicated domains and legitimate cloud storage. This evolving staging setup makes it particularly challenging for defenders to establish effective infrastructure-based blocking or network controls. We attribute this activity to a threat cluster we are tracking as UNC7017.
Based on available telemetry, impacted organizations spanned diverse sectors, including IT services, telecommunications, higher education and related entities in Australia, Brazil, India, Pakistan, Portugal, Singapore, South Africa, Spain, Switzerland, Türkiye, and the United States. That said, because the campaign attempted to deliver malware to any system polling the update distribution servers during the threat actor’s tampering windows, victimology was opportunistic and likely extends more broadly than the organizations we directly identified.
This campaign was initially identified through collaborative research with the ManageEngine Threat Analysis Lab (METAL), part of Zoho Corporation, whose endpoint detection and response (EDR) telemetry first detected the activity in late May across multiple customer environments. We thank the METAL team for their proactive telemetry sharing and ongoing collaboration to help secure our mutual customer bases and the broader software ecosystem. Following this joint effort, GTIG notified potentially affected organizations and shared technical findings with AOMEI Technology. AOMEI reported that they took corrective action to secure their distribution servers. METAL’s analysis of this campaign is available in their blog .
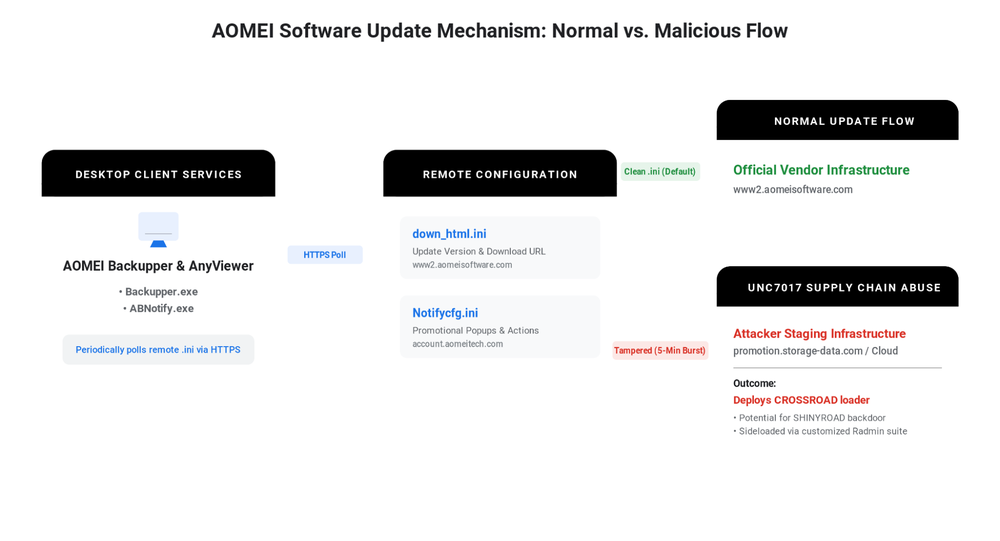
AOMEI Backupper provides data backup, disk cloning, and disaster recovery, while AnyViewer facilitates remote desktop access and support. Users of these products rely on the ABMarket update flow and its associated background services ( Backupper.exe and ABNotify.exe ) that periodically poll remote endpoints over HTTPS for update notifications and promotional pop ups:
Update Configuration ( down_html.ini ): The software periodically sends an HTTPS request to https://www2.aomeisoftware.com/download/abpopup/down_html.ini . This file contains the version number, the MD5 hash of the expected update package, and the URL where the client should download upgrade-now.zip .
Notification Configuration ( Notifycfg.ini ): The software contacts https://account.aomeitech.com/Notifycfg.ini . This file instructs the local notification process ( ABNotify.exe ) what messages to display and specifies commands or programs located in the software’s local directory to execute.
Under normal conditions, these files direct the client to download official files hosted on AOMEI’s own domain ( www2.aomeisoftware.com ).
Cryptographic Security & Key Generator
Generate entropy-tested high-security keys and encryption-grade tokens.
Source: Cloud Blog.
Read the full story at the original source ↗
For questions: mrsmithcons@gmail.com.
❓ Frequently Asked Questions (Cloud Architecture Briefing)
What makes this Cloud Architecture feature significant for FreeSky Cloud readers?
Our editorial team tracks verified source corroboration, technical specifications, and cultural resonance to deliver comprehensive analytical coverage.
How frequently is this coverage updated?
Our 24/7 automated monitoring desk updates breaking developments, verified media telemetry, and community commentary in real-time.
Where can readers follow ongoing developments on Investigating Ephemeral Supply Chain Tampering?
Bookmark this page or subscribe to our verified RSS feed for instant breaking alerts and in-depth analyses.
☁️ Complete Cloud Credit Application Guide & Architecture Specs
Direct application templates, fast-track partner codes, and architecture benchmarks.
⚡ Access Cloud Playbook ➔More from FreeSky Cloud
Nvidia CEO Urges U.S.-China Talks Over Potentially Dangerous A.I.
Nvidia CEO Jensen Huang is calling for greater dialogue between the United States and China over artificial in...
Even Seoul National University Can't Fill Its Science Graduate Programs, and HD Hyundai Bets on AI Power | October 16 2026
Seoul National University left 41.4% of its science and engineering graduate programs under-filled over five y...
Ukraine unveils flying ambulance drone that could save lives in minutes
Ukraine unveils flying ambulance drone that could save lives in minutes A Ukrainian company has demonstrated a...
 🔭 FreeSky Cosmos
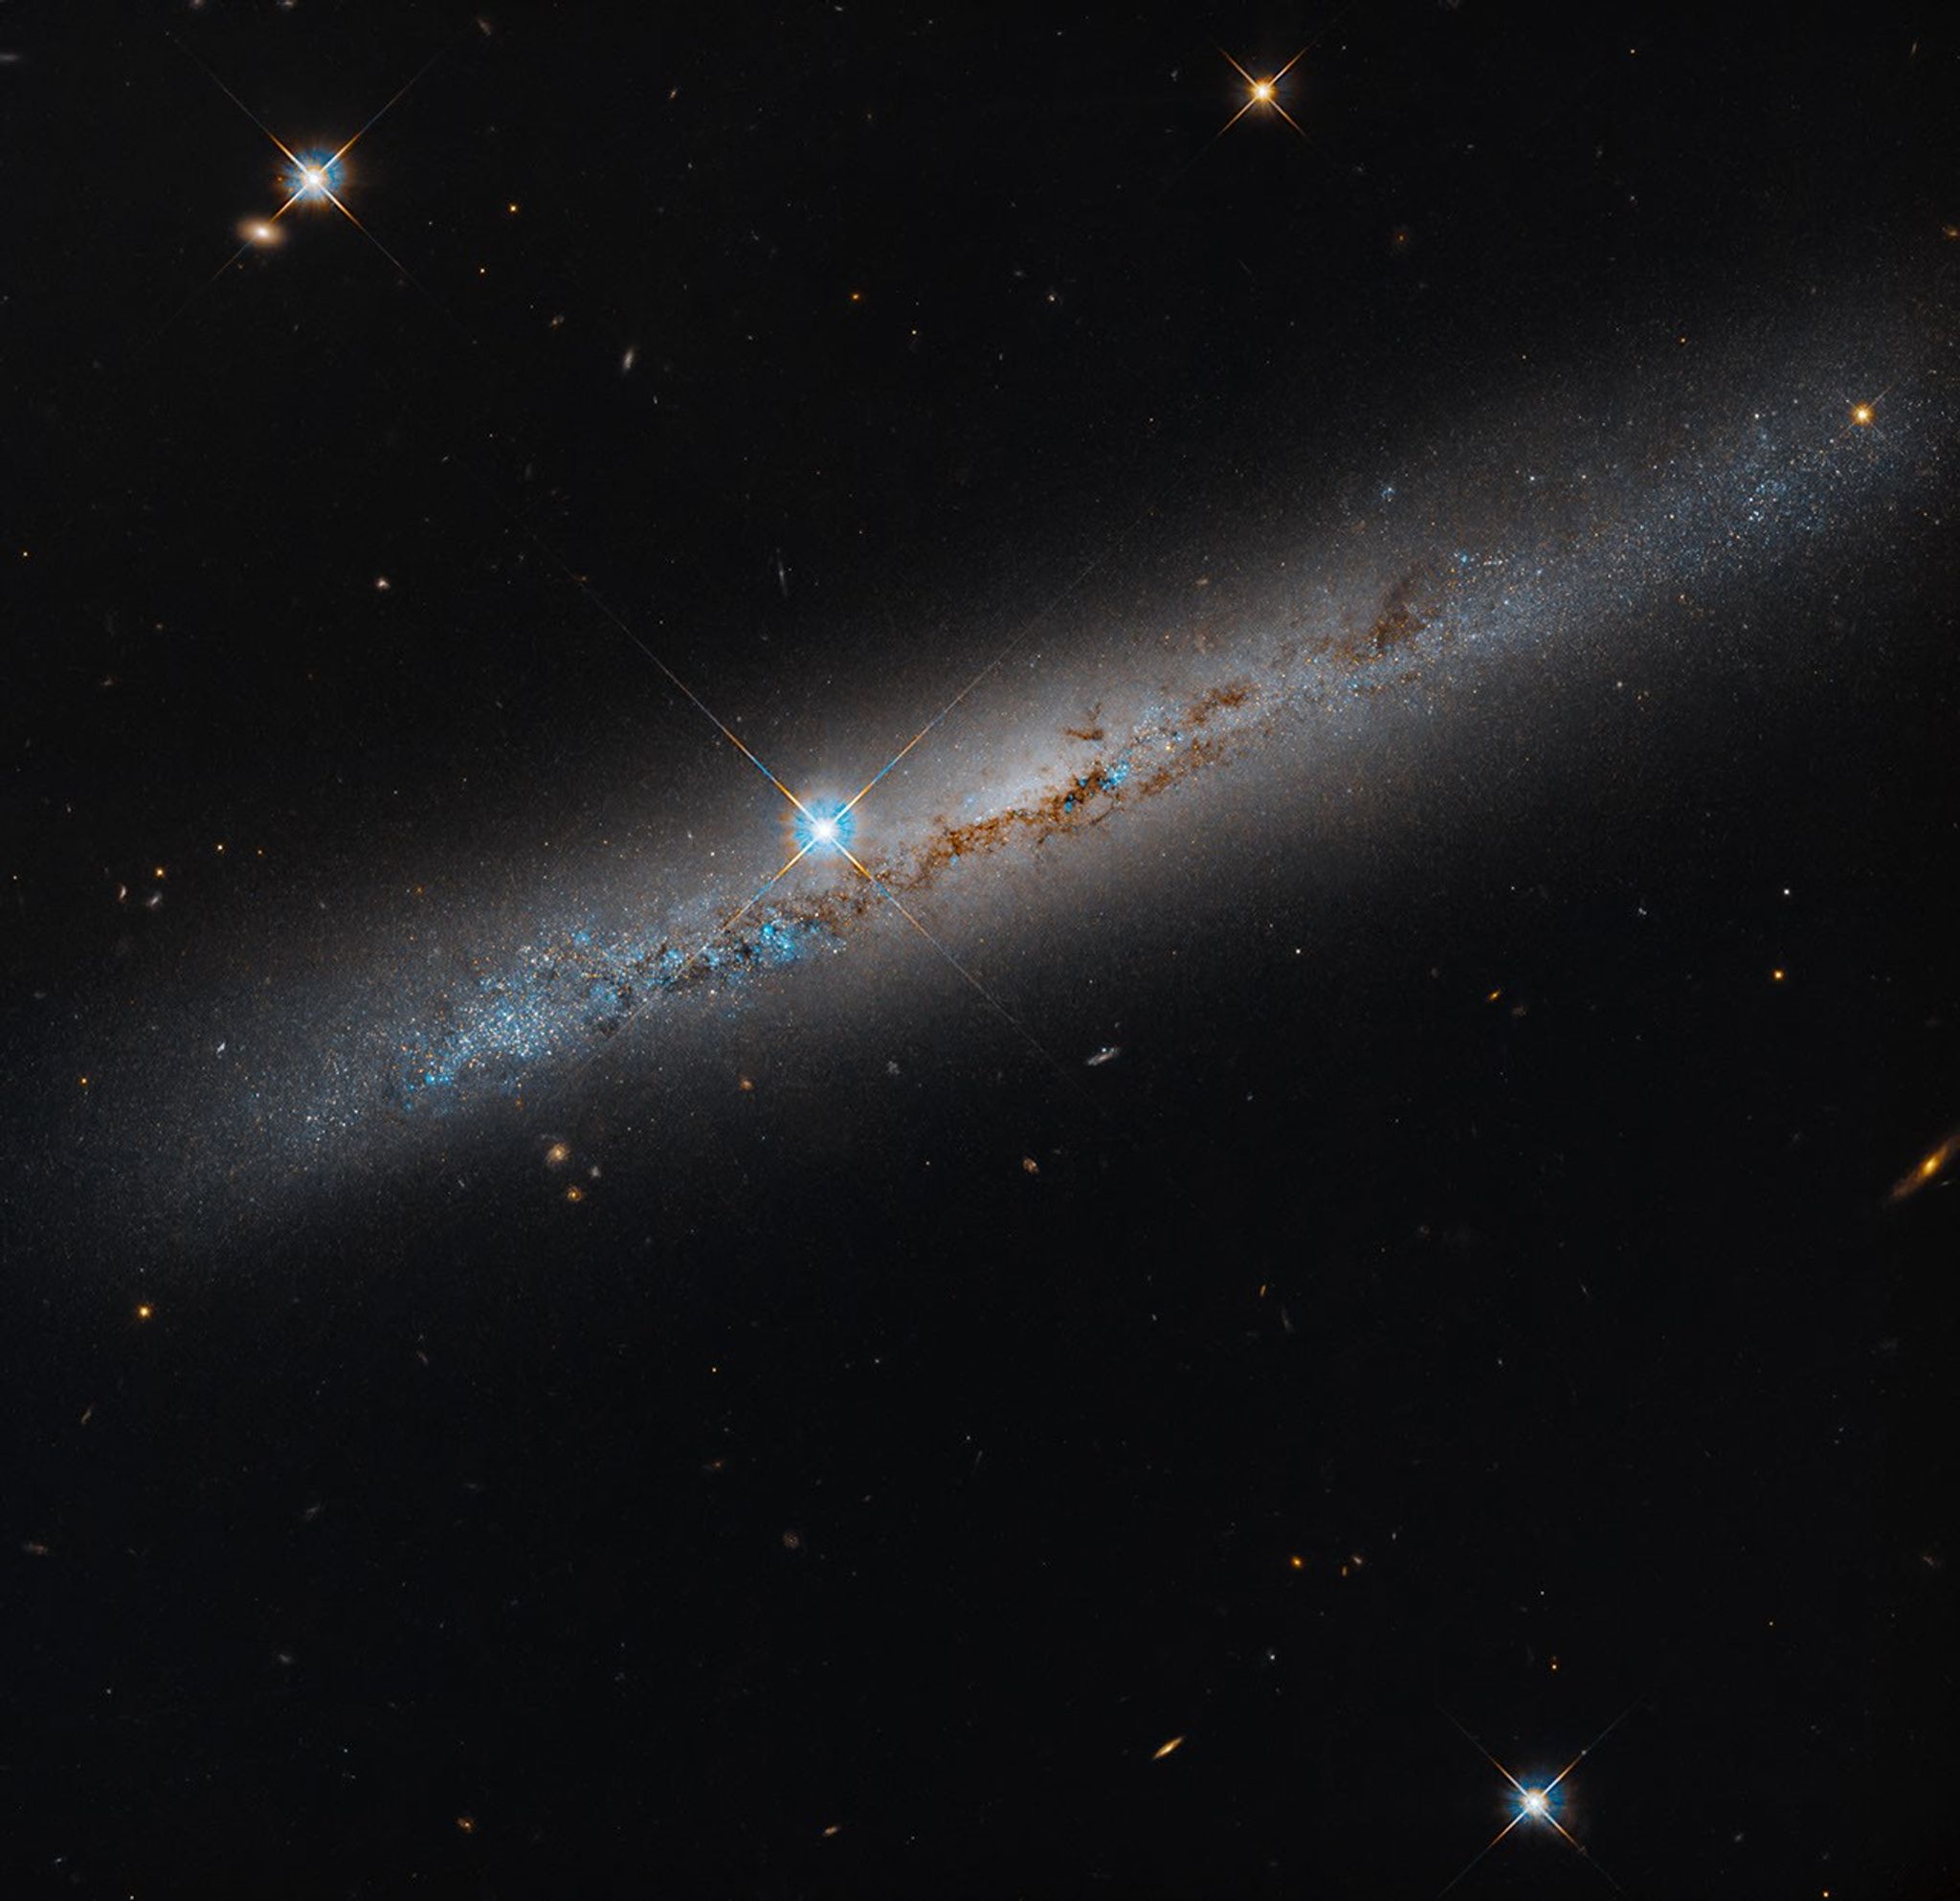
NASA’s Hubble Spies Spiral’s Edge
This NASA Hubble Space Telescope image features the edge-on, intermediate spiral galaxy NGC 1827, located roug...